BitLocker Recovery Key Backup
Summary
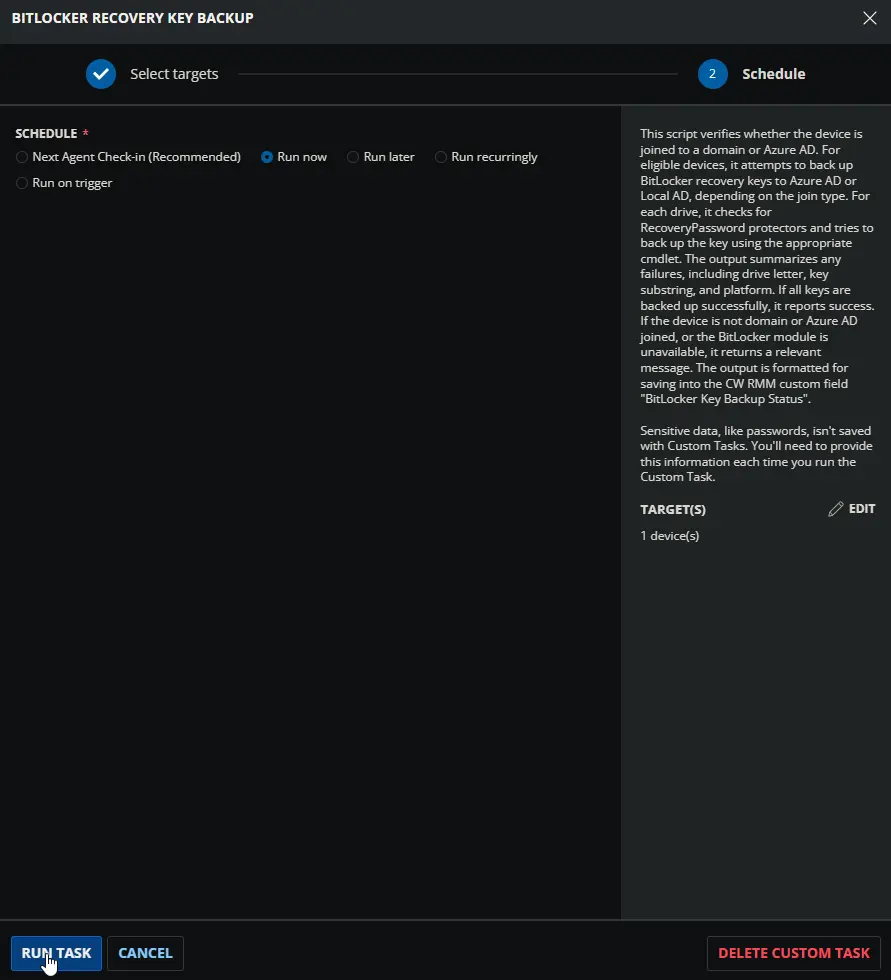
This script verifies whether the device is joined to a domain or Azure AD. For eligible devices, it attempts to back up BitLocker recovery keys to Azure AD or Local AD, depending on the join type. For each drive, it checks for RecoveryPassword protectors and tries to back up the key using the appropriate cmdlet. The output summarizes any failures, including drive letter, key substring, and platform. If all keys are backed up successfully, it reports success. If the device is not domain or Azure AD joined, or the BitLocker module is unavailable, it returns a relevant message. The output is formatted for saving into the CW RMM custom field BitLocker Key Backup Status.
Notes: The BitLocker Drive Encryption feature must be enabled on servers to run this script against windows servers. Auditing will not work without enabling this feature.
Sample Run
Dependencies
- Custom Field - BitLocker Key Backup Status
- Group - BitLocker Key Backup Enabled
- Solution - BitLocker Key Backup
Task Setup Path
Tasks Path: AUTOMATION ➞ Tasks
Task Type: Script Editor
Task Creation
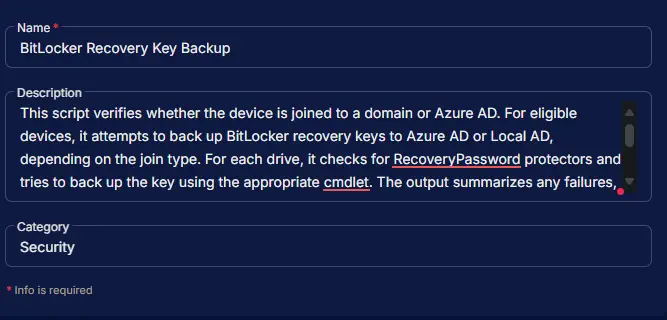
Description
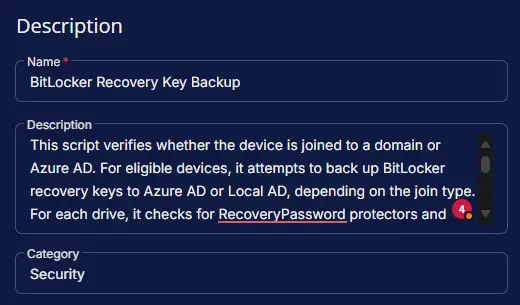
- Name:
BitLocker Recovery Key Backup - Description:
This script verifies whether the device is joined to a domain or Azure AD. For eligible devices, it attempts to back up BitLocker recovery keys to Azure AD or Local AD, depending on the join type. For each drive, it checks for RecoveryPassword protectors and tries to back up the key using the appropriate cmdlet. The output summarizes any failures, including drive letter, key substring, and platform. If all keys are backed up successfully, it reports success. If the device is not domain or Azure AD joined, or the BitLocker module is unavailable, it returns a relevant message. The output is formatted for saving into the CW RMM custom field "BitLocker Key Backup Status". - Category:
Security
Script Editor
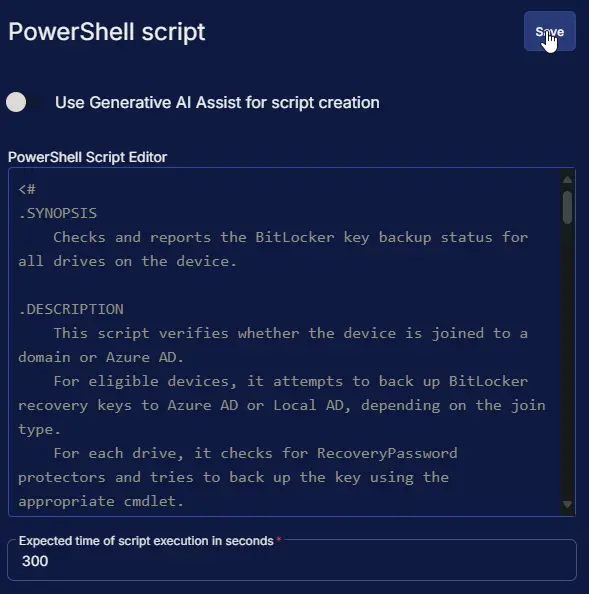
Step 1: Row -> PowerShell script
- Use Generative AI Assist for script creation:
False - Expected time of script execution in seconds:
300 - Operating System:
Windows - Continue on Failure:
False - Run As:
System - PowerShell Script Editor:
Step 2: Row -> Script Log
- Script Log Message:
%Output% - Continue on Failure:
False - Operating System:
Windows

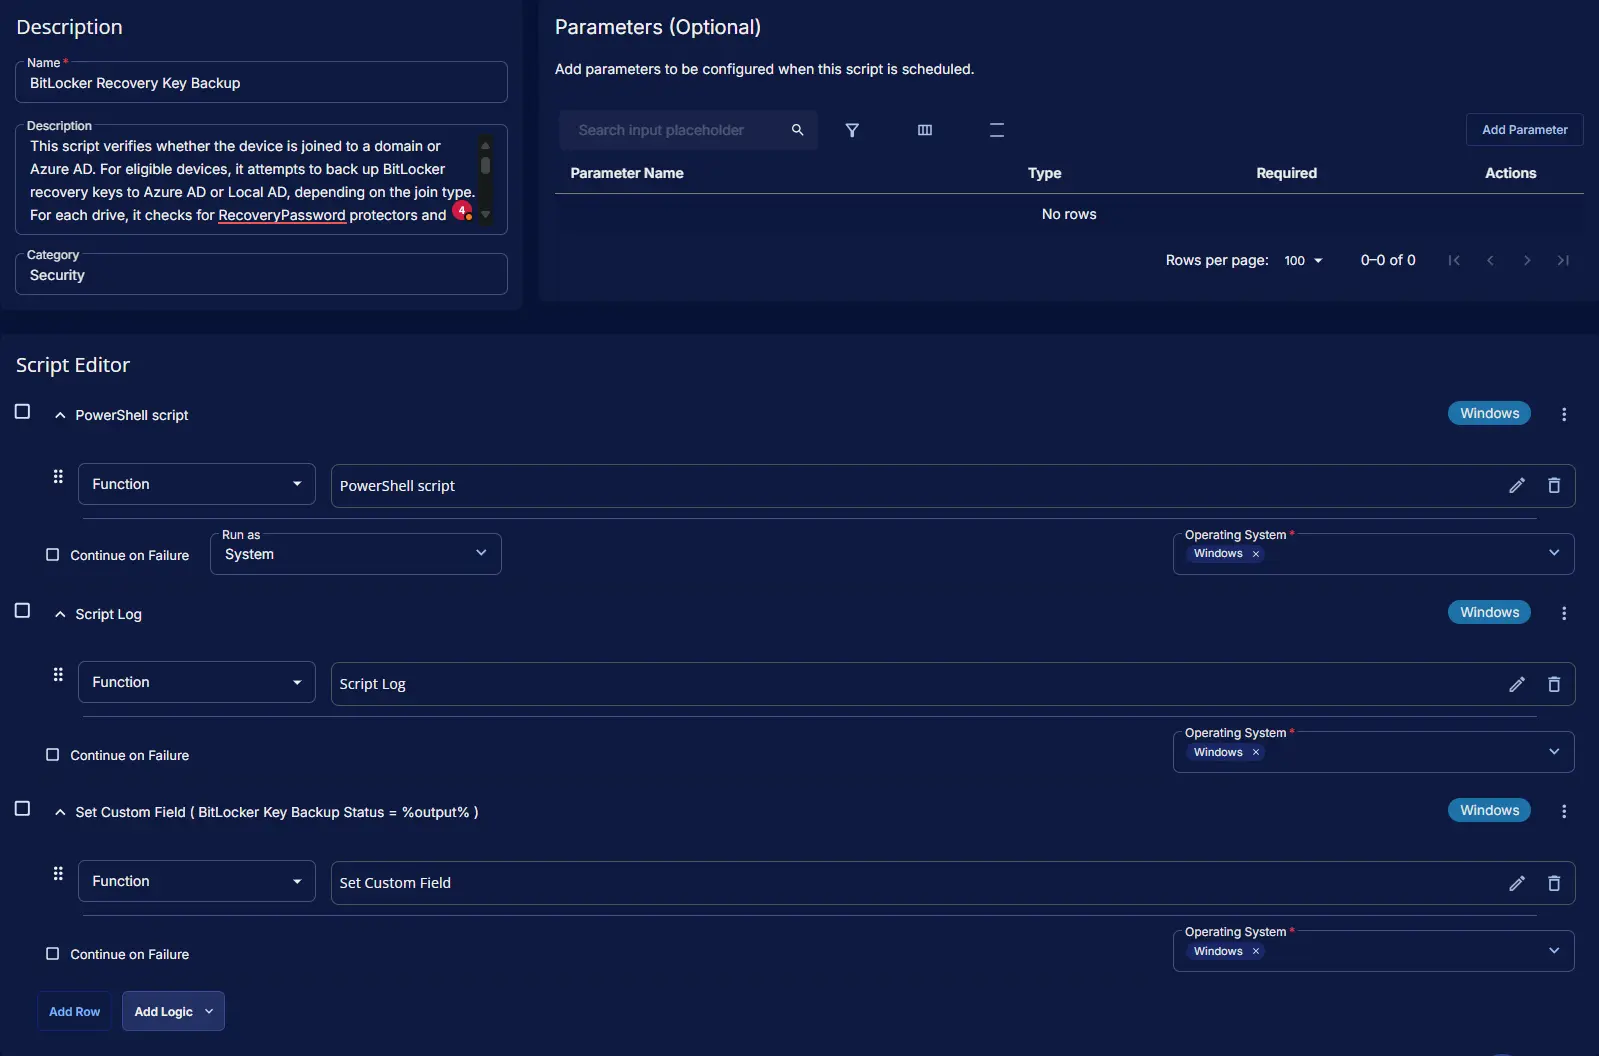
Step 3: Row -> Set Custom Field ( BitLocker Key Backup Status = %output% )
- Custom Field:
BitLocker Key Backup Status - Value:
%Output% - Continue on Failure:
False - Operating System:
Windows

Completed Task
Output
- Script Log
- Custom Field
Schedule Task
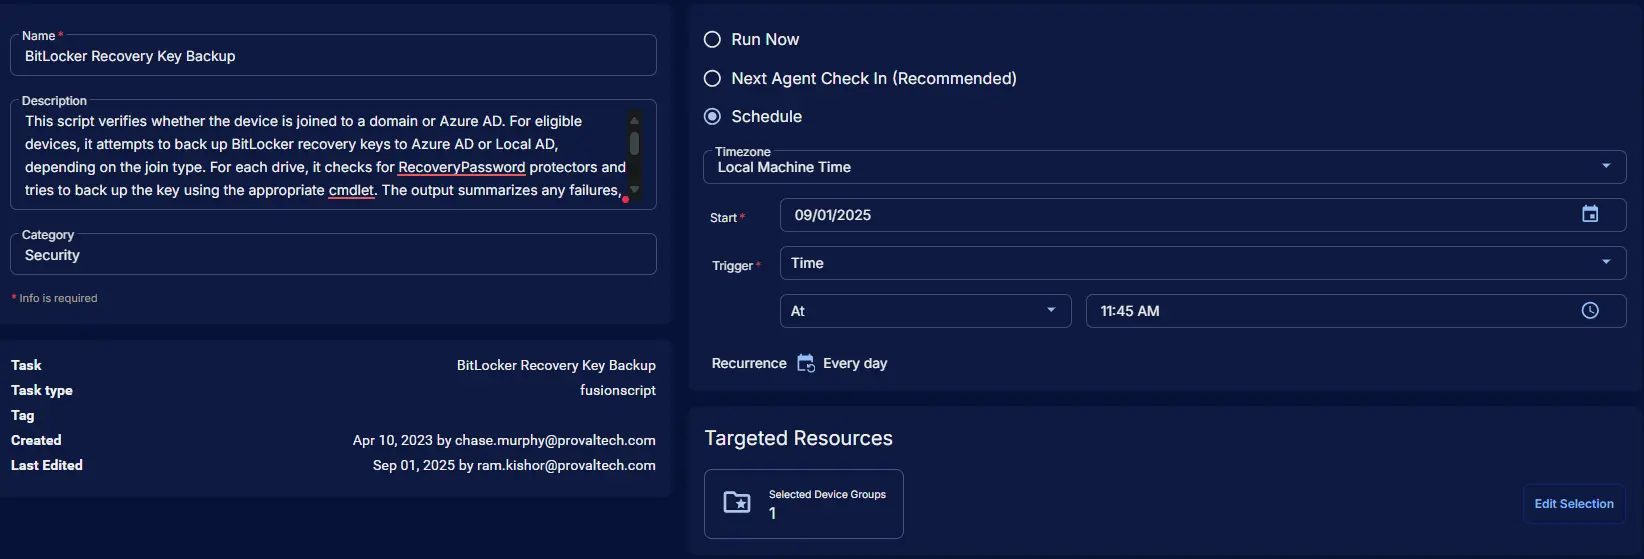
Task Details
- Name:
BitLocker Recovery Key Backup - Description:
This script verifies whether the device is joined to a domain or Azure AD. For eligible devices, it attempts to back up BitLocker recovery keys to Azure AD or Local AD, depending on the join type. For each drive, it checks for RecoveryPassword protectors and tries to back up the key using the appropriate cmdlet. The output summarizes any failures, including drive letter, key substring, and platform. If all keys are backed up successfully, it reports success. If the device is not domain or Azure AD joined, or the BitLocker module is unavailable, it returns a relevant message. The output is formatted for saving into the CW RMM custom field "BitLocker Key Backup Status". - Category:
Security
Schedule
- Schedule Type:
Schedule - Timezone:
Local Machine Time - Start:
<Current Date> - Trigger:
TimeAt<Current Time> - Recurrence:
Every day

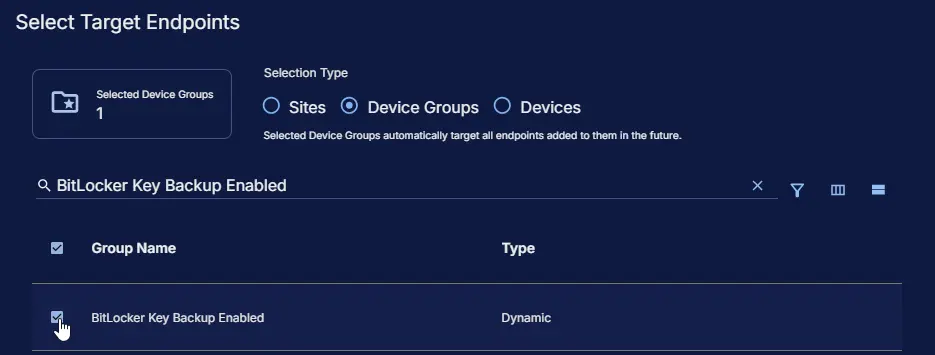
Targeted Resource
Device Group: BitLocker Key Backup Enabled
Completed Scheduled Task
Changelog
2025-09-01
- Initial version of the document