Enforce TLS SSL Hardening
Overview
Enforces Windows TLS/SSL security hardening by disabling legacy protocols, enabling supported modern TLS versions, configuring .NET strong cryptography settings, disabling specified TLS cipher suites, and optionally initiating or prompting for a required system reboot.
Implementation
-
Download the component from the
datto-rmmrepository: -
After downloading the file, click on the
Importbutton in the Datto RMM interface. -
Select the component just downloaded and add it to the Datto RMM interface.
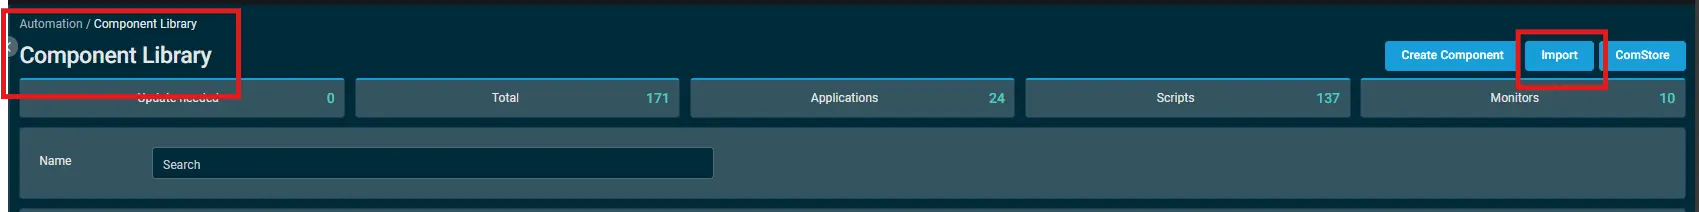
-
After Importing the component to the Datto RMM, make sure to add the component to the
PVALGroup always.- Steps to Add the component under
PVALGroup.
i. Click onDrop Down Icon.
ii. Click onAdd to Group.

iii. Select the group asPVAL
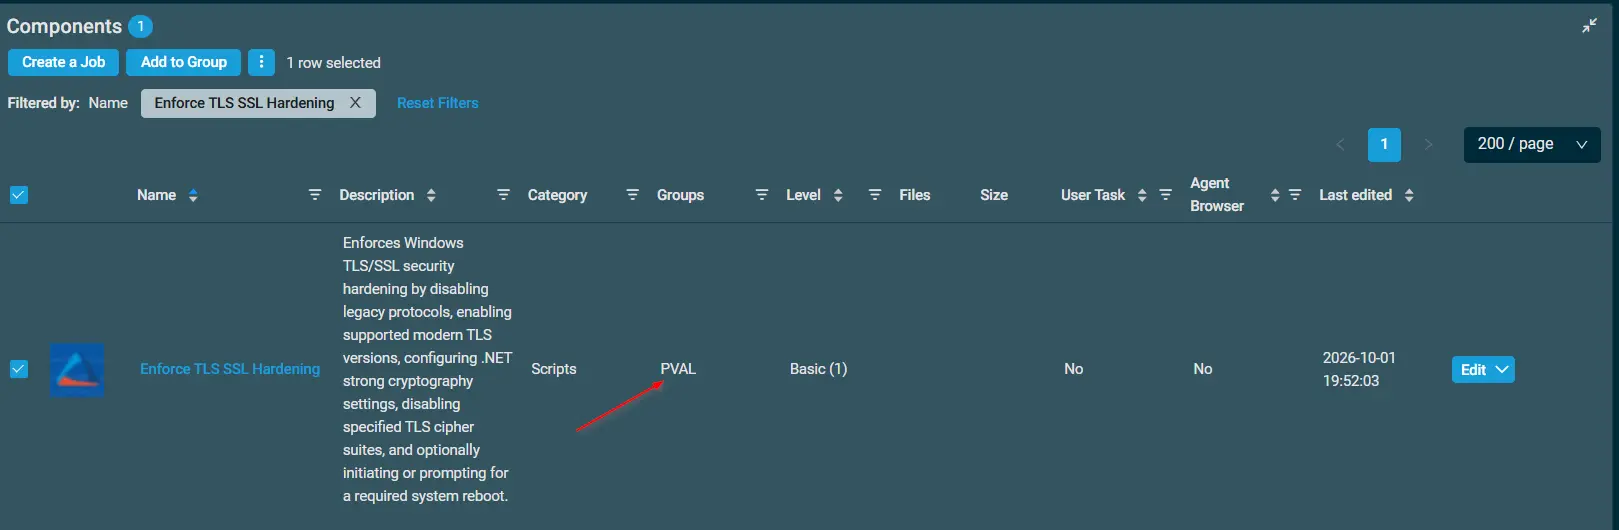
- Steps to Add the component under
Sample Run
To execute the Enforce TLS SSL Hardening over a specific machine, follow these steps:
-
Select the machine you want to run the
Enforce TLS SSL Hardeningon from the Datto RMM. -
Click on the
Quick Jobbutton.
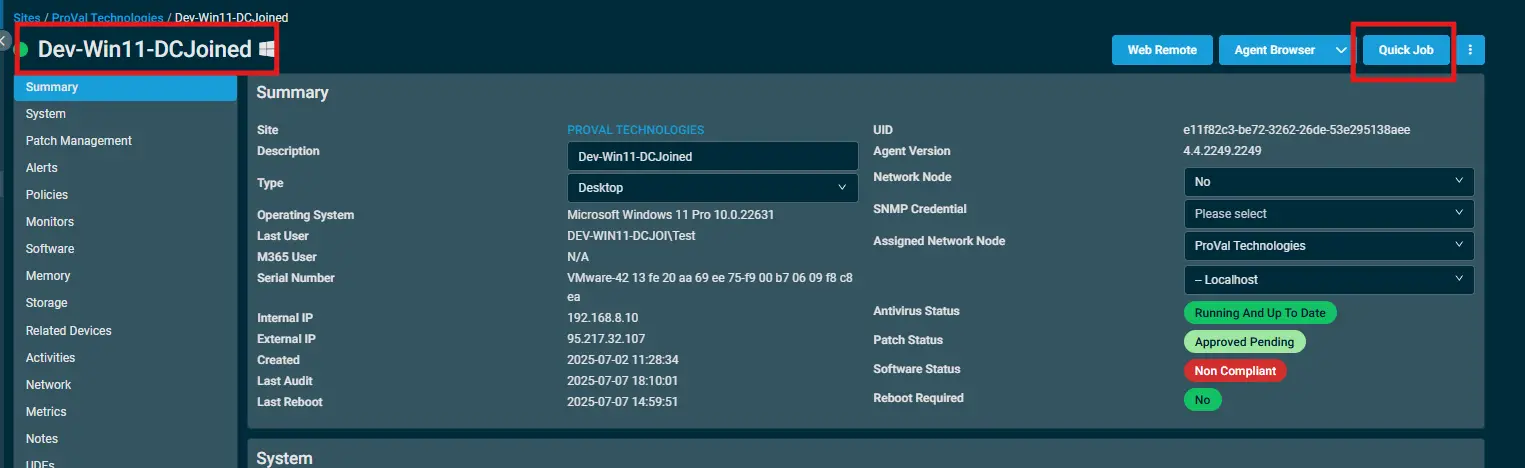
-
Search the component
Enforce TLS SSL Hardeningand click onSelect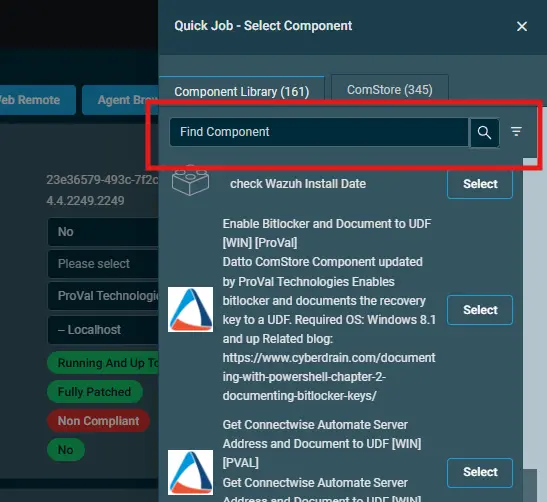
-
Click on
Runto execute the script:
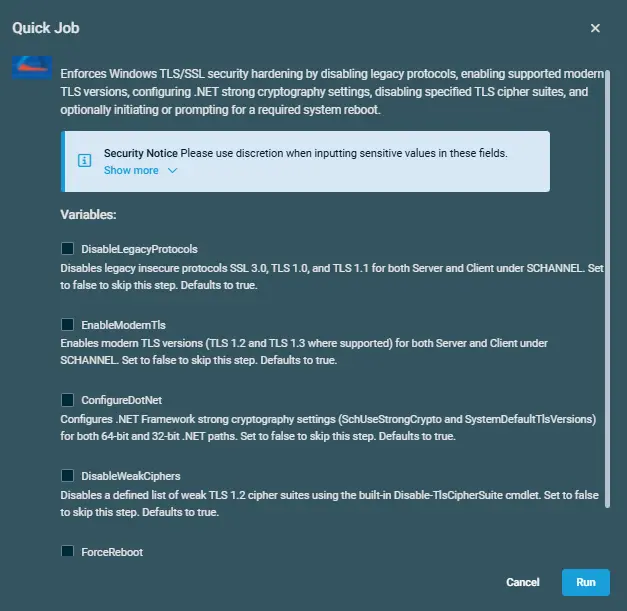
Datto Variables
| Variable Name | Type | Default | Description |
|---|---|---|---|
DisableLegacyProtocols | Boolean | False | Set to true to disable SSL 3.0, TLS 1.0, TLS 1.1 |
EnableModernTls | Boolean | False | Set to true to enable TLS 1.2 and TLS 1.3 |
ConfigureDotNet | Boolean | False | Set to true to configure .NET strong crypto |
DisableWeakCiphers | Boolean | False | Set to true to disable weak cipher suites |
ForceReboot | Boolean | False | Select this option to reboot the machine and apply the changes immediately |
Output
- stdOut
- stdError
Attachments
Changelog
2026-10-07
- Added environment variables to independently control protocol, TLS, .NET, cipher, and reboot settings, along with improved OS detection and execution output.
2026-09-16
- Initial version of the document